The attack that hit refrigerated display cases in hundreds of French supermarkets during the night of 11-12 October 2026 is presented as a notable example of physical damage caused by poorly protected remote OT access. According to the source material, the affected controllers were in many cases directly reachable from the Internet, with publicly documented vulnerabilities and, in part of the fleet, products already at end of life. ANSSI’s final technical conclusions on the vulnerability actually exploited had not yet been published at the time of the article.
The technical issue starts with the plant architecture. In a supermarket, the system manager coordinates local controllers, defrost cycles, measurements and alarms, and its web interface is commonly used for service access. Based on the reconstructions cited, attackers are said to have changed defrost setpoints to as much as 50 °C and extended cycle duration from one to eight hours. In other words, the attack appears to have abused a legitimate function outside its intended operating limits, resulting in a broken cold chain and destroyed goods.
The article points to three Claroty Team82 vulnerabilities documented for Danfoss AK-SM 800A units and patched in 2025: an authentication bypass, a command injection flaw and a weakness allowing changes to web-server configuration. For older models such as the AK-SM 800 and AK-SC255/355, the problem shifts to support status: firmware updates are no longer available and migration had already been recommended by the manufacturer. The proposed attack path remains an informed reconstruction rather than a publicly confirmed forensic finding.
The broader message is that this is framed as a systemic OT issue, not just an isolated product story. Legacy connected controllers, third-party maintenance, incomplete asset inventories and remote access left open for convenience create a repeatable exposure pattern across refrigerated logistics, food processing, HVAC and building management. The source also stresses the lack of independent physical limits and of a separate line of defense outside the same controller that commands the process.
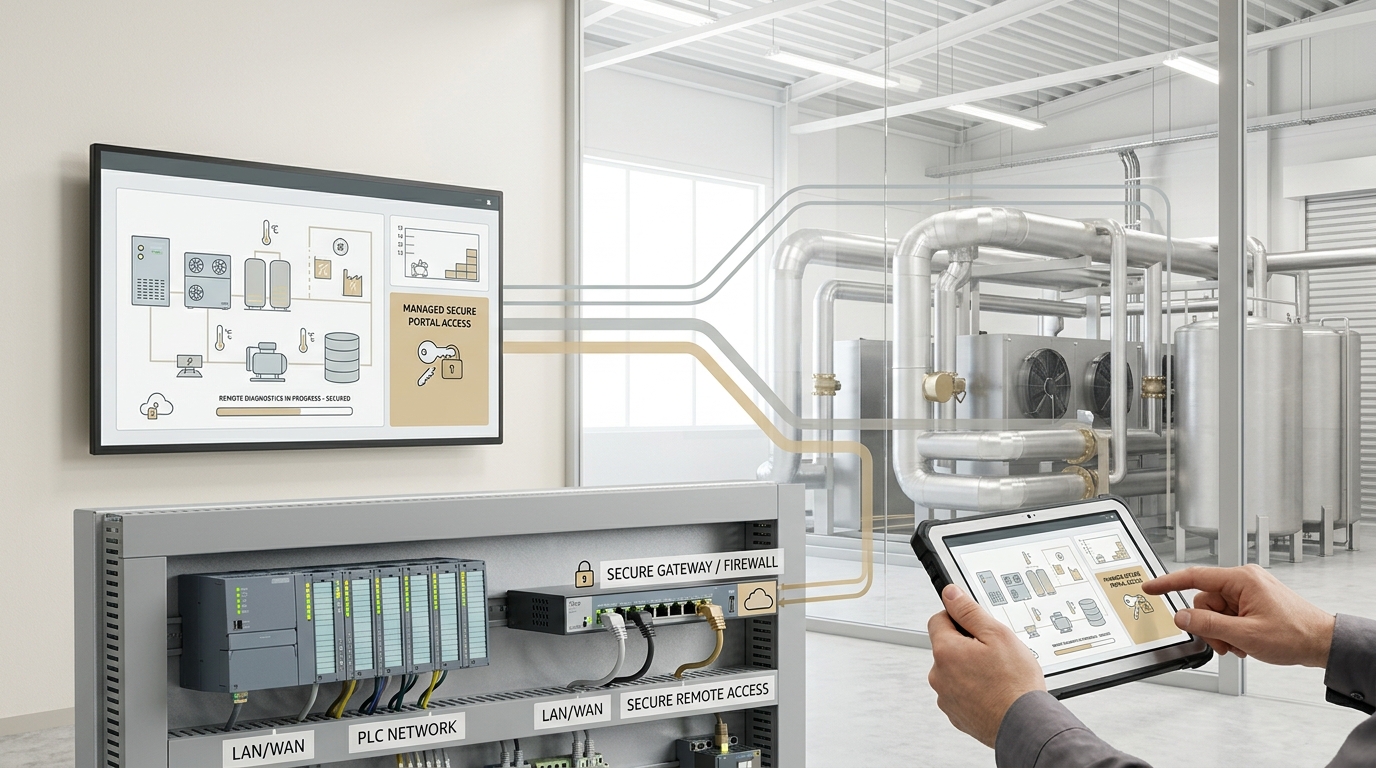
For Italian industry, the article links the case to the installed base of interconnected assets financed under the 4.0 and Transition 5.0 framework. It argues that the incentive’s interconnection requirement concerns interoperability, not Internet exposure. The risk emerges when remote maintenance, remote diagnostics and remote control are implemented through vendor portals, industrial routers or firewall openings without any formal check on how that access is protected. In this context, law 199/2025, described as in force for 2026-2028 in the source, extends eligibility to industrial firewalls, IEC 62443-aligned segmentation, access gateways and software for continuous monitoring and automated response.
The practical takeaway is that removing direct exposure does not in itself break interconnection with factory systems, but remote access then needs to be replaced by governed architectures, named sessions, multi-factor authentication and tightly limited privileges. For companies buying or operating connected machinery and plant, OT access security cannot be treated as a minor installation detail.